Preparation starts with real decisions
A customer asks for TISAX evidence, the assessment approaches, and suddenly every employee is assigned a course. That produces a completion list, but not necessarily reliable behaviour. Can purchasing assess an unusual request for information? Does reception know who may collect a visitor? Can engineering recognise when a file transfer must stop? These are the decisions that TISAX employee training should address. The following practice plan is intended for suppliers and service providers in Germany. It is a recommended local approach, not an official ENX curriculum.
Do not begin with memorised interview answers. Employees should be able to explain how they actually work and find the relevant instruction. An honest question is preferable to a confidently stated but incorrect rule. Separating awareness from specialist competence lets organisations train the wider workforce appropriately while giving process owners additional depth. The distinction between employee awareness and auditor training helps with this purchasing decision, but responsibilities within the company’s own information security management system still need explicit owners.
What a course can and cannot establish
TISAX combines assessment of information security management with controlled exchange of assessment results. According to the ENX process description, participants and the assessment scope are registered first, an approved audit provider is selected, and the assessment is carried out. Results can then be shared with selected partners. A learning module replaces neither this process nor operational and technical safeguards. An individual course completion record therefore does not establish that the organisation holds a TISAX label or satisfies every customer requirement.
The ENX Participant Handbook also explains that ENX currently offers no official training directly or through third parties and does not endorse the quality of external training services. Evaluate providers through their content, sources and stated limitations. For a business in Germany, contractual customer requirements, the assessment scope and applicable legal obligations must be considered separately. A request for a TISAX result does not by itself establish a universal statutory duty to take one particular course or repeat it at a fixed interval.
First establish scope, catalogue version and ownership
Before assigning training, the responsible owner records which sites, activities and information are involved and which assessment objectives are being agreed. Do not copy another company’s course plan without adaptation. The ENX announcement on ISA2027 distinguishes publication from applicability: the new catalogue was published in 2026 and applies to assessments ordered from 1 January 2027. Confirm the specific transition with the audit provider. Publication of a new edition does not automatically mean that every ongoing assessment immediately switches to it.
Record the catalogue edition used, the date its source was checked, and the person responsible for translating changes into learning needs. The ISA catalogue provides the assessment baseline; this article does not replace reviewing it. Then map each relevant activity to a learning objective, a responsible manager and evidence. Engineering needs different cases from reception or purchasing. Managers also need practice in exceptions, resources and escalation. A general course for everyone can provide a shared foundation, but it does not cover every role.
A role matrix with four clear handovers
For engineering and project leads, the learning objective is to establish protection needs and the approval route before sharing information. The information owner decides permitted use; the sender checks the recipient and channel. Evidence should not be a statement such as “privacy understood”, but a reasoned decision about a fictional document. Ask who resolves an unclear classification and which activity must wait. Use the organisation’s actual terminology and approved sharing tools so participants can transfer the exercise directly into their work.
For purchasing and sales, focus on disclosure to business partners. The business team describes the need, information security reviews the protection arrangements, and an authorised owner approves the transfer. For reception and facilities, key handovers involve registration, identity checks, escorting and returning access credentials. Managers handle urgency and exceptions: who decides when the usual owner is absent, who records the rationale, and when must an activity remain blocked? These are recommended local responsibilities, not universally prescribed job titles.
 AI-generated
Practice case 1: the urgent engineering drawing
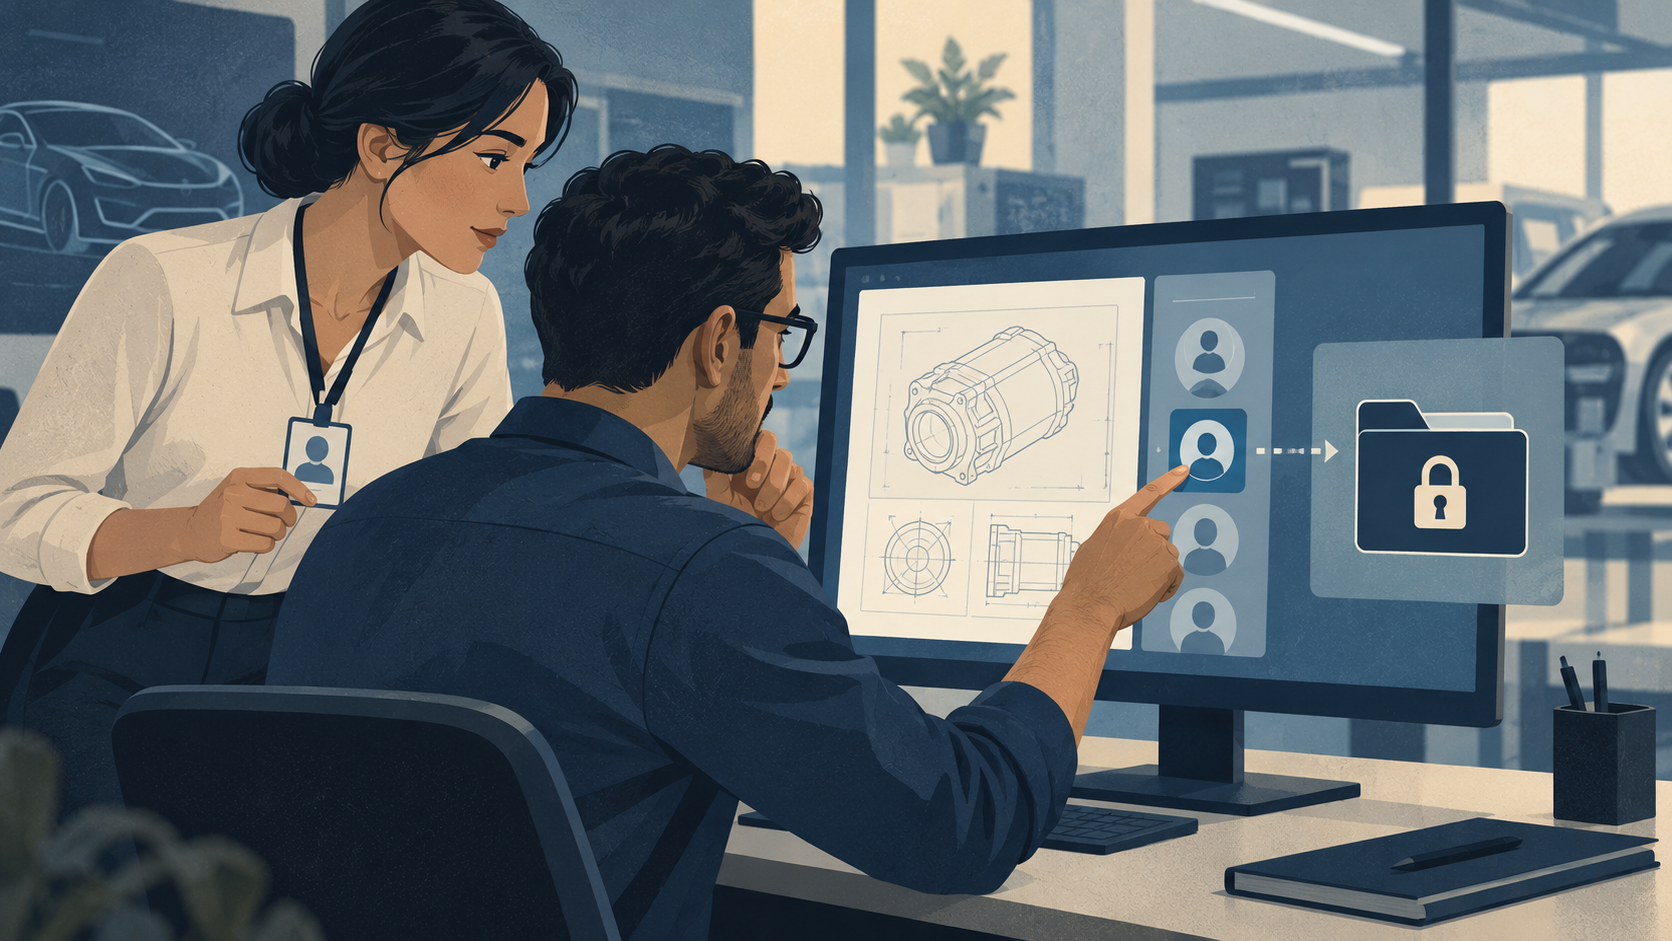
A fictional customer writes near the end of the day: the usual portal is unavailable, so the latest drawing should go to a personal address. A familiar signature is not sufficient authorisation. Start the exercise with a pause: verify the request through a known contact route, involve the information owner and offer an approved transfer method. If authorisation remains unclear, do not send. The trainer then changes only the urgency, preventing participants from memorising an obviously unusual email address as the entire answer.
Connect this case to phishing reporting behaviour: the goal is not flawless detection of every manipulation, but timely escalation of uncertainty to the right person. A second round introduces supposed approval from senior management. Practice around social engineering explains why rank and urgency cannot replace a controlled process. Assess whether employees can offer a safe alternative and explain their decision. Simple detection scores for suspicious messages capture only part of that ability and can overlook useful escalation behaviour.
Practice case 2: access and work tools
A new colleague urgently needs access to a project folder. Another employee offers their own password because the formal access approval is missing. Ask the group to identify the permitted route: request personal access, establish ownership and consider an approved interim arrangement. Shared credentials do not solve an organisational gap. Reinforce passwords, MFA and passkeys without suggesting that any single authentication method solves the entire security problem. Finish only when participants also know the deputy who handles the request during absence.
Vary the case with a publicly available AI tool: an employee wants a confidential customer report summarised. Start with data approval, the permitted service and the intended use, not the most convenient prompt. Guidance on safe AI use helps identify unofficial workflows early. The training team should never copy real partner information into a demonstration. Synthetic documents with fictional names and drawings are enough to practise the decision without creating a new disclosure risk inside the training exercise itself.
 AI-generated
Practice case 3: visitors and visible information
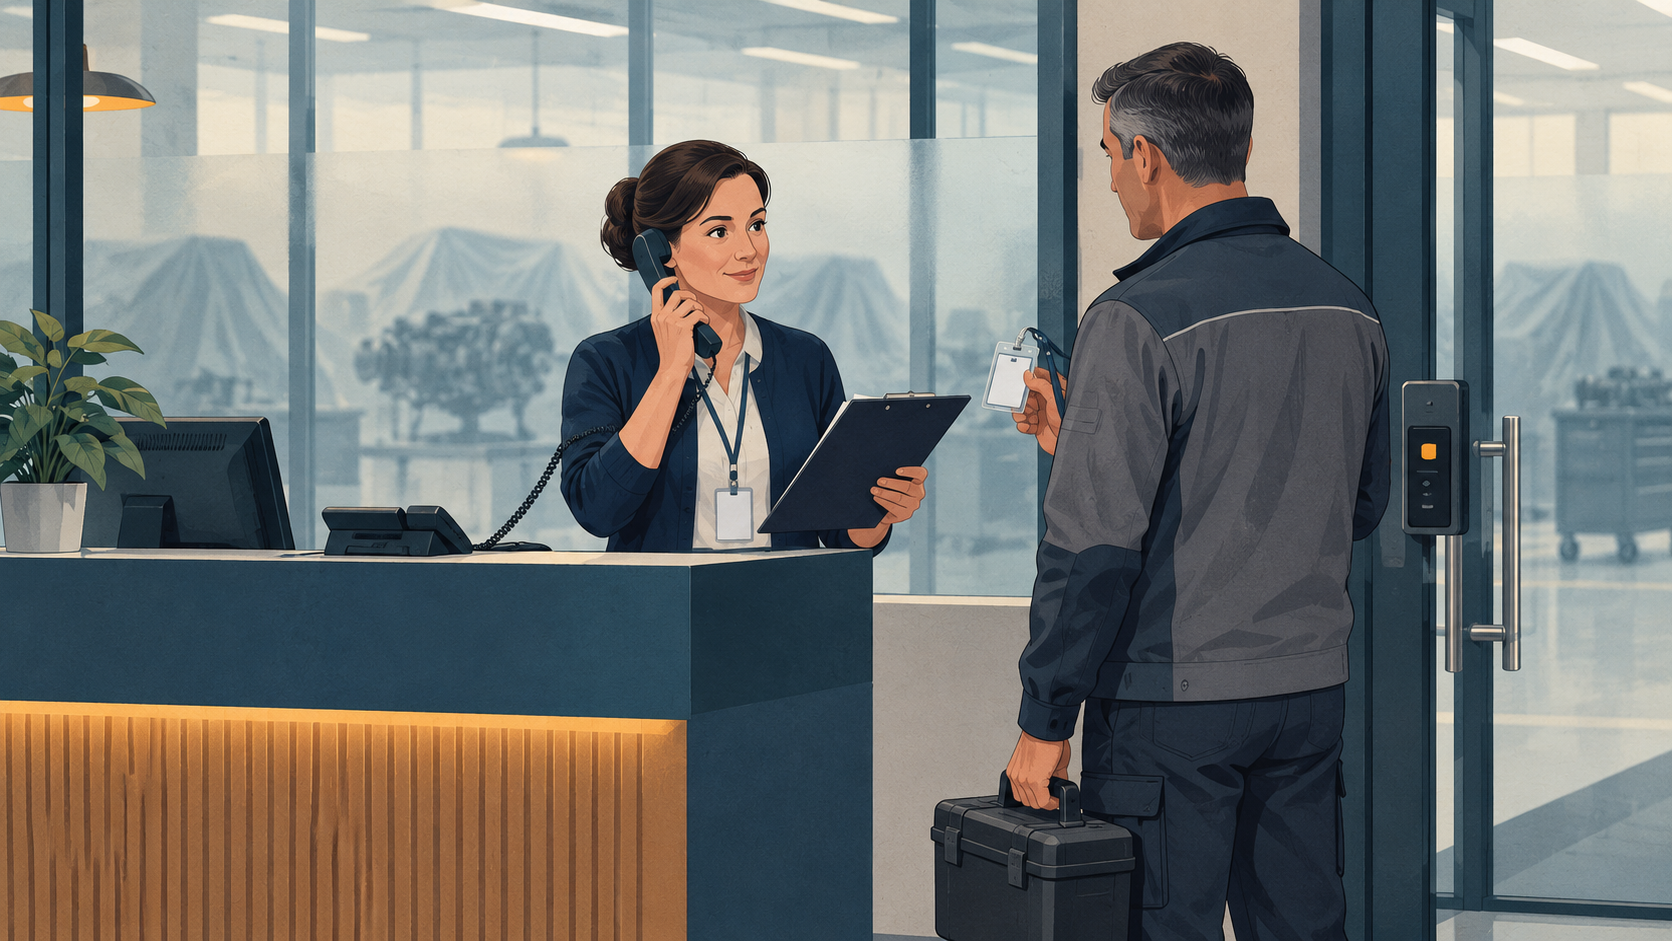
A service technician arrives without an appointment and names a familiar contact. In the role-play, reception checks the assignment through an internal contact rather than relying only on a phone number supplied by the visitor. Until clarified, the visitor remains in the designated area. The host then checks routes, visible documents and local photography restrictions. Special prototype rules depend on agreed protection requirements and scope; not every office visit is automatically a prototype-protection case. Employees should explain these distinctions using their own areas.
Practice case 4: notice an error and report it
An employee notices that a project-folder link may have broader access than intended. The first task is not legal analysis, but prompt internal reporting with the time, affected system and observed sharing setting. The responsible team takes further action under the incident process. Employees should not independently delete evidence, hunt for blame or run unfamiliar repair tools. Ransomware response behaviour provides additional scenarios for suspicious IT activity. Any statutory notification duties require a separate professional assessment; an internal report does not replace that review.
Turn practice into usable evidence
For each session, record the target group, content version, date, owner, participation and observed learning objective. Capture unresolved questions and agreed follow-up rather than collecting green completion indicators alone. Structured training records help organise this evidence but do not replace review of its substance. Access to personal learning information should be limited to its intended purpose. Retention is determined through applicable evidence obligations and local rules, not an invented universal TISAX retention period.
A practical local launch plan starts with a short role check, followed by a shared foundation session and a workplace exercise with a debrief. Revisit critical cases after process changes or identified uncertainty. This sequence and the chosen intervals are organisational recommendations, not prescribed assessment dates. Pay particular attention to shift changes, new starters and external personnel performing relevant tasks. Missing participation remains an open action; passing an online quiz alone does not demonstrate that an operational handover works.
The debrief must also expose process gaps
Prepare four review questions for the facilitator: is sensitive information recognised, is authorisation actually checked, is a permitted next step chosen, and is the reporting or approval contact reachable? Record the answers separately. Someone may correctly identify a risk yet be blocked by a missing contact. That is not automatically a learning failure. The real gap might be a deputy arrangement, a reachable reporting channel or a usable work instruction. Assign an owner and a verifiable completion condition to that gap.
For example, three shift teams correctly report a questionable external sharing request, but only the day shift receives an answer. Additional mandatory modules will not fix that availability problem. Process owners must first organise the handover, then have employees practise the revised workflow. Change the details in the second round so that participants cannot merely repeat a familiar answer. The debrief records what changed in the process and how the team can recognise the improvement during ordinary work.
Accuracy matters more than a green indicator when handling partner evidence as well. Train purchasing to forward a customer request to the responsible internal owner: which partner is asking, which service is involved, and which scope is intended? A course certificate does not answer a question about an organisation’s assessment result. Employees should not reinterpret these documents or promise external recognition themselves. Authorised owners determine which information may be shared through the intended exchange mechanism and whether it covers the actual request.
Make exercises accessible in both language and organisation. Employees without individual office computers still need a workable way to find instructions and contacts. Where several working languages are used, the local reporting instruction must be understandable as well as the course itself. Ask participants to describe the next step in their own words and actually locate the contact. This checks usability better than flawless repetition of technical terms. Use results to improve behaviour and workflows, not to publicly embarrass individuals in the team.
Choose a proportionate next step
ConformBase’s TISAX awareness course describes the fundamentals, information classification, and handling of prototype and partner data. Use an offering of this kind as a starting point for shared terminology, then add your own approval routes, contacts and exercises. Before purchasing, check that the content and version fit the learning need. An individual completion record is evidence of learning, not official ENX training or a TISAX label. What matters is that employees can make safe decisions and the organisation operates its safeguards effectively.
ConformBase
Turn knowledge into training that works.
Bring compliance, privacy and security awareness into a format your people want to complete, with certificates and audit-ready evidence.
Start free trialAsk about custom courses →