The Evolution of Social Engineering: From Phishing Emails to Synthetic Media
The threat landscape of information security has changed drastically in recent years. While classic attacks were often easy to recognize by grammatical errors or clumsy phrasing in emails, the rapid progress of artificial intelligence now enables highly precise attacks. Attackers use sophisticated algorithms to manipulate voices and faces in real time. This development presents companies with completely new challenges, as visual and auditory cues that we instinctively trust can now be manipulated. In our comprehensive Security Awareness topic world, we demonstrate how important continuous awareness of these modern threat patterns has become in daily work. Additional context is available in Security Awareness topic world. For the broader process, see Social Engineering at Work: The Risky Decisions Training Should Cover.
Federal authorities warn urgently against this new quality of social engineering. According to analyses by the Federal Office for Information Security (BSI), criminals increasingly use emotional manipulation to bypass technical security barriers. The psychological component is often more decisive than technological finesse. When an employee believes they are speaking directly with executive management, the inhibition threshold to disregard established security guidelines drops. A sound understanding of these mechanisms is therefore the first step in effectively protecting one's organization from the dangers of AI-supported manipulation. A useful deeper dive is Phishing Training: Why Reporting Behavior Matters More Than Perfect Detection.
- Classic phishing indicators are losing relevance due to generative AI.
- Synthetic media exploits basic human trust in voice and image.
- Security authorities like the BSI call for an adaptation of organizational defense methods.
 AI-generated
Voice Cloning in Daily Operations: When the Boss's Voice Deceives
So-called voice cloning, the artificial replication of a human voice, has reached a frightening level of precision. For a deceptively real copy, attackers often need only a few seconds of audio material, extracted for example from public presentations, interviews, or social media posts. In a business context, this technology is used to fake telephone instructions for urgent transfers. These attacks, which are closely related to classic CEO-Fraud und Zahlungsbetrug, specifically rely on the fact that employees in stressful situations do not question the voice of a known executive. Acoustic familiarity overrides natural skepticism.
Technically speaking, neural networks analyze the specific characteristics of a voice such as pitch, speaking rate, and individual emphasis. During a call over conventional telephone lines or low-quality VoIP connections, minimal digital artifacts are hardly noticeable. Attackers systematically exploit these quality losses to disguise the artificial nature of the voice. For companies, this means that the mere acoustic identification of a person on the phone no longer represents a sufficient security guarantee. Additional, procedural security levels must be established that function independently of the voice.
Video Deepfakes: Manipulation in Real-Time Conferences
Even more complex and dangerous are video deepfakes, where a person's face and facial expressions are overlaid in real time onto an attacker's video feed. In virtual meetings, this can lead employees to believe they are interacting with their real colleagues or supervisors, while in truth they are speaking with an impostor. Although creating real-time video fakes requires high computing power, the technology has become so accessible that even less experienced criminals can use corresponding tools. To protect against such attacks, a targeted Deepfakes erkennen Kurs for the workforce is one of the most effective preventive measures.
However, there are technological and visual indicators that can point to a fake. These include unnatural blinking behavior, blurring at the edges of the face, asymmetrical lip movements relative to the spoken word, or strange light reflections in the eyes. Sudden head movements can also cause the algorithm to lose alignment for a brief moment, allowing the attacker's original face to shimmer through. Employees must be trained to pay attention to these subtle details and, in case of doubt, ask targeted questions that an attacker cannot answer on the spot.
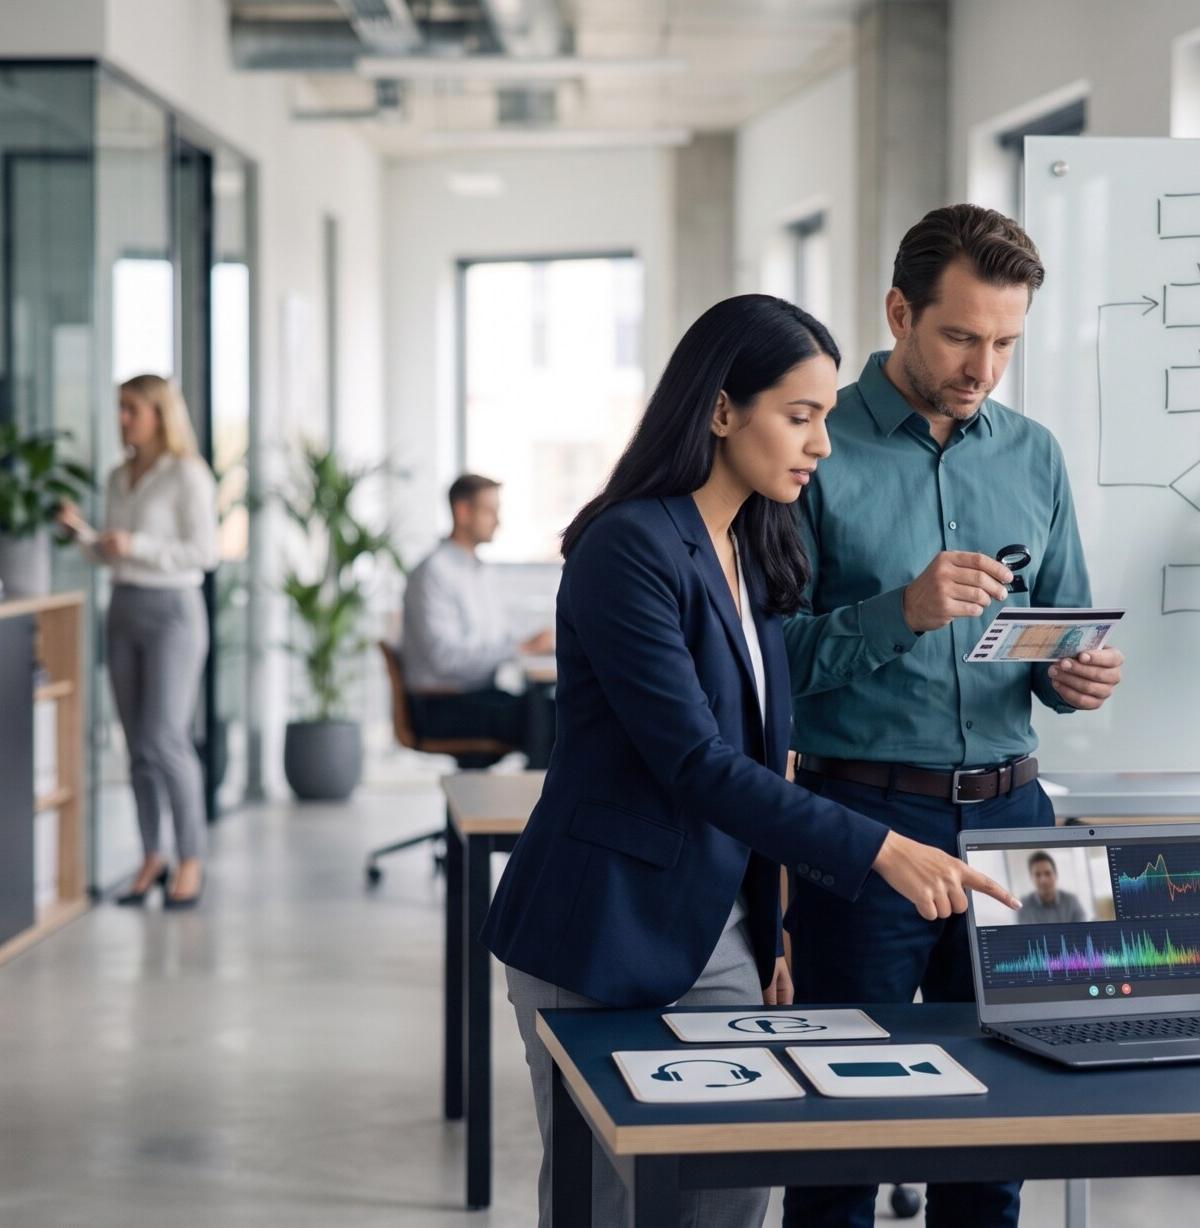 AI-generated
The Psychology of Pressure: How Attackers Manipulate Teams
The success of deepfake attacks is rarely based solely on the technical quality of the fake. Rather, perpetrators use psychological levers such as artificial urgency, strict secrecy, and the demonstration of authority. A typical scenario is the alleged emergency in which an urgent acquisition or a confidential payment must be processed immediately, otherwise severe damage to the company is threatened. This enormous stress blocks the logical thinking of those affected, and established control mechanisms are deliberately bypassed. In our practical Social Engineering Kurs, teams learn to see through these psychological manipulation patterns early on and to react calmly even under pressure.
Psychological research shows that people in hierarchies tend to execute instructions from supposedly higher-ranking individuals without verification. Attackers exploit this obedience by posing as board members or external auditors. They often demand absolute discretion to prevent the victim from consulting with colleagues. As soon as an employee is requested to bypass an established four-eyes principle, all alarm bells must ring. No business urgency justifies waiving basic security rules, and this awareness must be deeply anchored in the corporate culture.
Verification Frameworks: Processes Against AI Fraud
To protect themselves effectively against AI-supported attacks, companies must not rely solely on the attentiveness of their employees. Clear, binding verification processes are required. A central element is so-called out-of-band verification. If an unusual instruction is received via phone or video, confirmation must be obtained via a completely different, previously verified communication channel, for example via a known internal chat platform or through a personal callback to a number stored in the system. In addition, secret code words or security questions should be agreed upon for sensitive transactions that cannot be found on the internet or in emails.
In addition, technical guidelines for using communication tools must be continuously adapted. Employees should learn how to achieve a safe use of AI tools and which data they must never upload to external platforms under any circumstances to avoid providing attackers with material for voice cloning. Restrictive handling of publicly accessible audio and video data of executives makes it significantly harder for criminals to create high-quality deepfakes. The combination of technical prevention, clear processes, and trained behavior forms the most effective protective shield against modern fraud schemes. For deeper training, safe use of AI tools is a useful fit.
Implementation and Continuous Training in the Enterprise
The introduction of security guidelines is only successful if they are actively lived and regularly reviewed. Static training sessions that take place only once a year are not sufficient given the rapid technological development. Companies should rely on interactive training formats that simulate real attack scenarios and give employees the opportunity to apply their knowledge practically. Whether a legal obligation to conduct such training exists depends on the respective industry, company size, and specific risk profile. Nevertheless, establishing such measures is a business necessity for almost every modern company to avert existential damage.
To determine the current maturity level of your own organization in the area of cybersecurity and to close vulnerabilities systematically, a systematic test run is recommended. You can now use our platform and 14 Tage testen to gain access to practical learning content and simulations specifically designed to defend against deepfakes and social engineering. Through continuous sensitization of the teams, the human firewall is strengthened and the risk of successful attacks is significantly minimized. Invest in your employees' knowledge, as they are the most important line of defense in the digital age.
Related ConformBase pages
- Deepfakes erkennen Kurs
- CEO-Fraud und Zahlungsbetrug
- safe use of AI tools
- Social Engineering Kurs
- Security Awareness topic world
- 14 Tage testen
Official sources
ConformBase
Turn knowledge into training that works.
Bring compliance, privacy and security awareness into a format your people want to complete, with certificates and audit-ready evidence.
Start free trialAsk about custom courses →