The Misunderstanding of Click Rates as the Sole Success Metric
In many organizations, the success of security awareness campaigns is mistakenly measured by a single, isolated metric: the click rate. There is a widespread and persistent belief that a declining click rate automatically translates to a higher level of security within the company. However, this assumption is a dangerous and costly fallacy. Even if the click rate in a simulated phishing campaign drops below two percent due to intensive training, a single careless click by one employee is enough to compromise the entire corporate network. Absolute avoidance of clicks is simply utopian in a dynamic, digitalized working environment. Humans make mistakes, especially when under stress or when confronted with highly sophisticated social engineering attacks. What happens immediately after the click or upon the first suspicion is far more critical for actual security. This is where a modern, behavior-based approach comes in, focusing on active reporting behavior, which is discussed in detail and practically within our Security Awareness topic world. Additional context is available in Security Awareness topic world. For the broader process, see Social Engineering at Work: The Risky Decisions Training Should Cover.
When an employee receives a suspicious email, their immediate reaction determines the further course and the potential damage of the attack. If the employee merely ignores the email or silently deletes it, the threat remains fully active for the rest of the organization. Other colleagues, who might be less trained or simply distracted, could fall for the exact same message. Only through an active, rapid report to the Security Operations Center (SOC) or the internal IT department is a collective defense mechanism set in motion. IT security can immediately block the malicious sender address, delete already delivered messages from other users' inboxes, proactively suspend affected accounts, and effectively prevent further damage. Therefore, a high and rapid reporting rate is far more valuable for an organization's resilience than a supposedly perfect detection rate that remains without subsequent action and communication. A useful deeper dive is Ransomware Awareness: The Behaviors Companies Should Actually Train.
 AI-generated
The Psychology of Reporting: Error Culture Over Punishment
The psychology behind employee reporting behavior is complex and often neglected in practice. Many employees feel a deep-seated fear of retaliation, disciplinary action, or simple embarrassment in front of their colleagues if they have to admit to clicking a suspicious link or entering sensitive data. A restrictive error culture dominated by punishment inevitably leads to security incidents being covered up or concealed. This gives attackers valuable time to spread undetected within the network, escalate privileges, and exfiltrate sensitive data. To minimize this risk, organizations must actively establish a positive, open security culture. Mistakes must not be punished but understood as valuable learning opportunities. A well-founded Phishing und Social Engineering Kurs helps to systematically raise workforce awareness, understand the psychological mechanisms used by attackers, and sustainably reduce the fear of making mistakes.
Detecting a professional phishing email is more difficult today than ever before, as attackers employ increasingly sophisticated methods, as clearly demonstrated by the official analyses and situation reports of the Federal Office for Information Security (BSI). Social engineering systematically exploits human behaviors and emotions such as urgency, respect for authority, helpfulness, or curiosity. When employees learn during training that reporting an error or a suspicion actively contributes to the security of the entire company and is explicitly encouraged, their willingness to cooperate increases significantly. The primary goal of any awareness measure must be to make the reporting process as positive, simple, and barrier-free as possible, so that employees act without hesitation and without fear of negative consequences in an emergency.
Dismantling Technical and Organizational Barriers
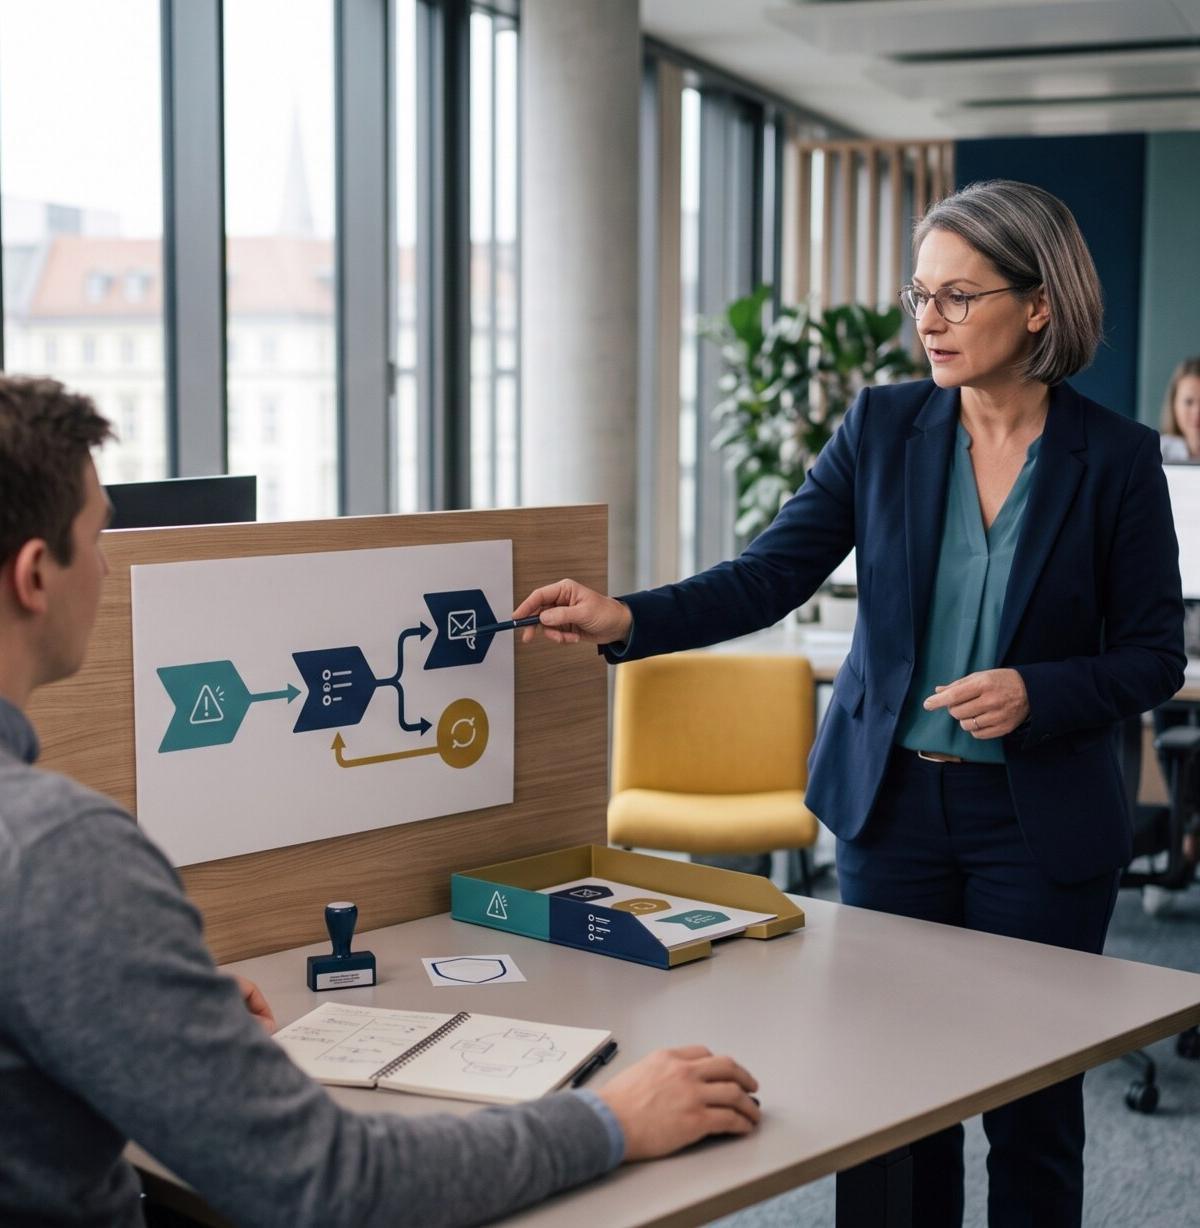
To sustainably improve reporting behavior in practice, technical and organizational barriers within the company must be systematically and consistently dismantled. A complicated, time-consuming reporting path, which, for example, requires manually forwarding emails as attachments to cryptic functional addresses or filling out complex ticketing system forms, immediately demotivates employees in their hectic daily work. Implementing a simple, intuitive phishing report button directly in the email client (such as Outlook or Gmail) is the undisputed best-practice approach here. With just a single click, a suspicious message can be transmitted directly to the responsible security team, automatically preserving all relevant email header information for analysis. This drastically reduces the barrier to entry for the employee and significantly accelerates the IT security response time.
In addition to the technical provision of the reporting button, the underlying organizational processes must be clearly defined and efficiently designed. Following a report, employees should receive timely, automated yet appreciative and informative feedback on whether the reported email was a false alarm, a harmless promotional email, or an actual threat. This immediate feedback reinforces positive reporting behavior through direct validation and simultaneously trains the employee's eye for future cases. The importance of structured, predefined processes in managing security incidents is taught in the specialized course Sicherheitsvorfaelle erkennen und melden, which prepares teams and employees to act quickly, coordinately, and flawlessly in an emergency.
 AI-generated
Threat Scenarios Beyond the Standard Email
Modern threat scenarios go far beyond the classic, easily recognizable mass phishing email with obvious spelling mistakes. Professional attackers use highly personalized and thoroughly researched methods to target specific decision-makers, administrators, or employees in finance departments. A particularly dangerous and financially devastating phenomenon is CEO fraud, where the identities of managing directors or board members are deceptively imitated to induce employees to authorize large wire transfers or release sensitive data. Detailed information on these highly specific attack vectors and effective organizational protective measures can be found in the section CEO-Fraud und Zahlungsbetrug. Since such attacks are often purely text-based and contain neither malicious links nor file attachments, technical filters fail almost completely here, making human vigilance and reporting behavior all the more critical.
Another massive risk to an organization's existence is the undetected infiltration of malicious software. Often, a single undetected access to an endpoint is enough to infect the entire corporate network with ransomware and completely encrypt business-critical systems. Comprehensive information on the prevention, detection, and defense against such threats is provided in the course Ransomware und Schadsoftware. Since detecting such highly specialized and often customized attacks is an enormous challenge even for experienced IT security experts, the rapid and uncomplicated reporting of even the smallest anomalies by vigilant employees is the company's most important and effective line of defense. If an employee immediately reports an unusual system process or a suspicious message, the spread of ransomware within the network can often be nipped in the bud.
Measuring Success: New KPIs for Security Culture
To realistically and data-drivenly evaluate the actual success of a security culture, organizations must move away from focusing solely on click rates and establish new, more meaningful Key Performance Indicators (KPIs). One of the most important metrics in this context is the reporting rate. It measures the percentage ratio of actually reported phishing emails to the total number of delivered test emails within a campaign. A continuously rising reporting rate is a clear indication that the workforce is actively participating in protecting the company and that the security culture is alive. Another critical and often underestimated KPI is the Mean Time to Report (MTTR). The faster the first report is received in the SOC after a phishing email is sent, the quicker the IT security team can react and initiate countermeasures for the entire organization.
Furthermore, the quality of incoming reports should be continuously analyzed. Do employees reliably distinguish between genuine spam, harmless newsletters, and actual, dangerous phishing attempts? A high quality of reports prevents overloading the Security Operations Center with countless false alarms and ensures that analysts can focus on real threats. Through the continuous and detailed analysis of this data, training measures within the company can be targeted and adjusted based on actual needs. Instead of repeatedly burdening the entire workforce with generic, boring content, departments with demonstrably low reporting rates or above-average response times can receive targeted and customized training, maximizing the efficiency of the entire security budget.
Enterprise Implementation and Regulatory Requirements
Implementing a reporting-centered training approach successfully requires a strategic and conscious decision by corporate management. Depending on the industry, regulatory requirements, and the individual risk profile of the company, very different legal or contractual evidence requirements may apply. For example, international standards such as ISO 27001 or modern regulatory mandates like the European NIS-2 Directive and DORA (Digital Operational Resilience Act) demand effective, verifiable training measures for employees as well as established incident response processes. However, whether a specific, legal training obligation exists always depends on the individual case, company size, and sector. Companies should therefore rely on flexible, scalable, and legally compliant platforms that integrate seamlessly into the existing compliance structure and deliver audit-proof evidence.
To make the entry into a modern, effective, and reporting-centered security awareness training as simple and efficient as possible, ConformBase offers a practical and intuitive platform that covers precisely these requirements. You can 14 Tage testen our comprehensive offering to personally convince yourself of the high quality, pedagogical depth, and practice-oriented approach of our courses. By combining easily understandable learning content, realistic phishing simulations, and a clear, motivating focus on active reporting behavior, you sustainably strengthen your company's digital resilience, protect your sensitive data from ransomware, and meet key regulatory compliance requirements at the touch of a button.
Related ConformBase pages
- Phishing und Social Engineering Kurs
- Sicherheitsvorfaelle erkennen und melden
- Security Awareness topic world
- CEO-Fraud und Zahlungsbetrug
- Ransomware und Schadsoftware
- 14 Tage testen
Official sources
ConformBase
Turn knowledge into training that works.
Bring compliance, privacy and security awareness into a format your people want to complete, with certificates and audit-ready evidence.
Start free trialAsk about custom courses →