An unusual payment reaches the back office on Friday afternoon. The relationship manager knows the customer well, but an explanation is missing. Effective anti-money laundering training means recording facts, passing them securely and respecting decision boundaries. This guide sets out a scenario exercise for financial firms operating in Germany and subject to the German Money Laundering Act, the GwG. It connects three roles around one case without turning employees into investigators. All examples are fictional and illustrate operational decisions rather than final assessments of actual transactions.
Start with scope and the learning objective
Before assigning a course, identify the relevant legal entity, activity and employee group. The obliged entities listed in section 2 GwG include different categories and exceptions; describing a business as a financial firm does not settle applicability. Within an institution, relationship management, payments operations and compliance may have different responsibilities for the same transaction. The learning objective is therefore not that everyone writes the same report. Each person should know what information to preserve, which internal channel to use and which decisions fall outside their authority. Where several entities are involved, the responsible team must also know which entity it represents.
Initial and ongoing employee instruction under section 6 GwG covers typologies, current methods and relevant duties, including data protection. This should not be turned into a blanket promise that one annual standard course satisfies every requirement. Set the scope, updates and practical additions according to the risks and responsibilities of your firm. The overview of mandatory employee training helps distinguish different legal foundations. This exercise assumes an approved internal escalation route, an available deputy and a current operating procedure. If any of those are missing, the first action is organisational: establish responsibility instead of disguising the gap with another knowledge quiz.
Separate responsibilities while sharing the case
The relationship manager records the trigger: what was requested, what explanation was provided and what inconsistency was noticed? They do not maintain a private suspicion file or discuss the matter in an open team chat. The back office adds the transaction status, internal references and existing documents without inventing an approval. The designated AML function assesses further handling, reporting obligations and necessary measures under the applicable rules. A named deputy takes over when the primary contact is absent. The sender also records receipt or uses the prescribed fallback route. A message sent without an accountable recipient is not yet an effective handover.
The same securities-related event may also raise suitability or conflict-of-interest questions. The practice cases for financial advice and back office address that WpHG perspective, but do not replace an AML assessment. Train parallel responsibilities without automatically sending every anomaly to the same queue. An incorrectly documented advice conversation does not, by itself, constitute a suspicious activity report. Conversely, a potential AML concern must not disappear because another compliance case already exists. The exercise record lists the responsible functions separately, linked through a common reference and an explicit decision about which information each function needs to perform its role.
Case one: A payment does not fit the customer profile
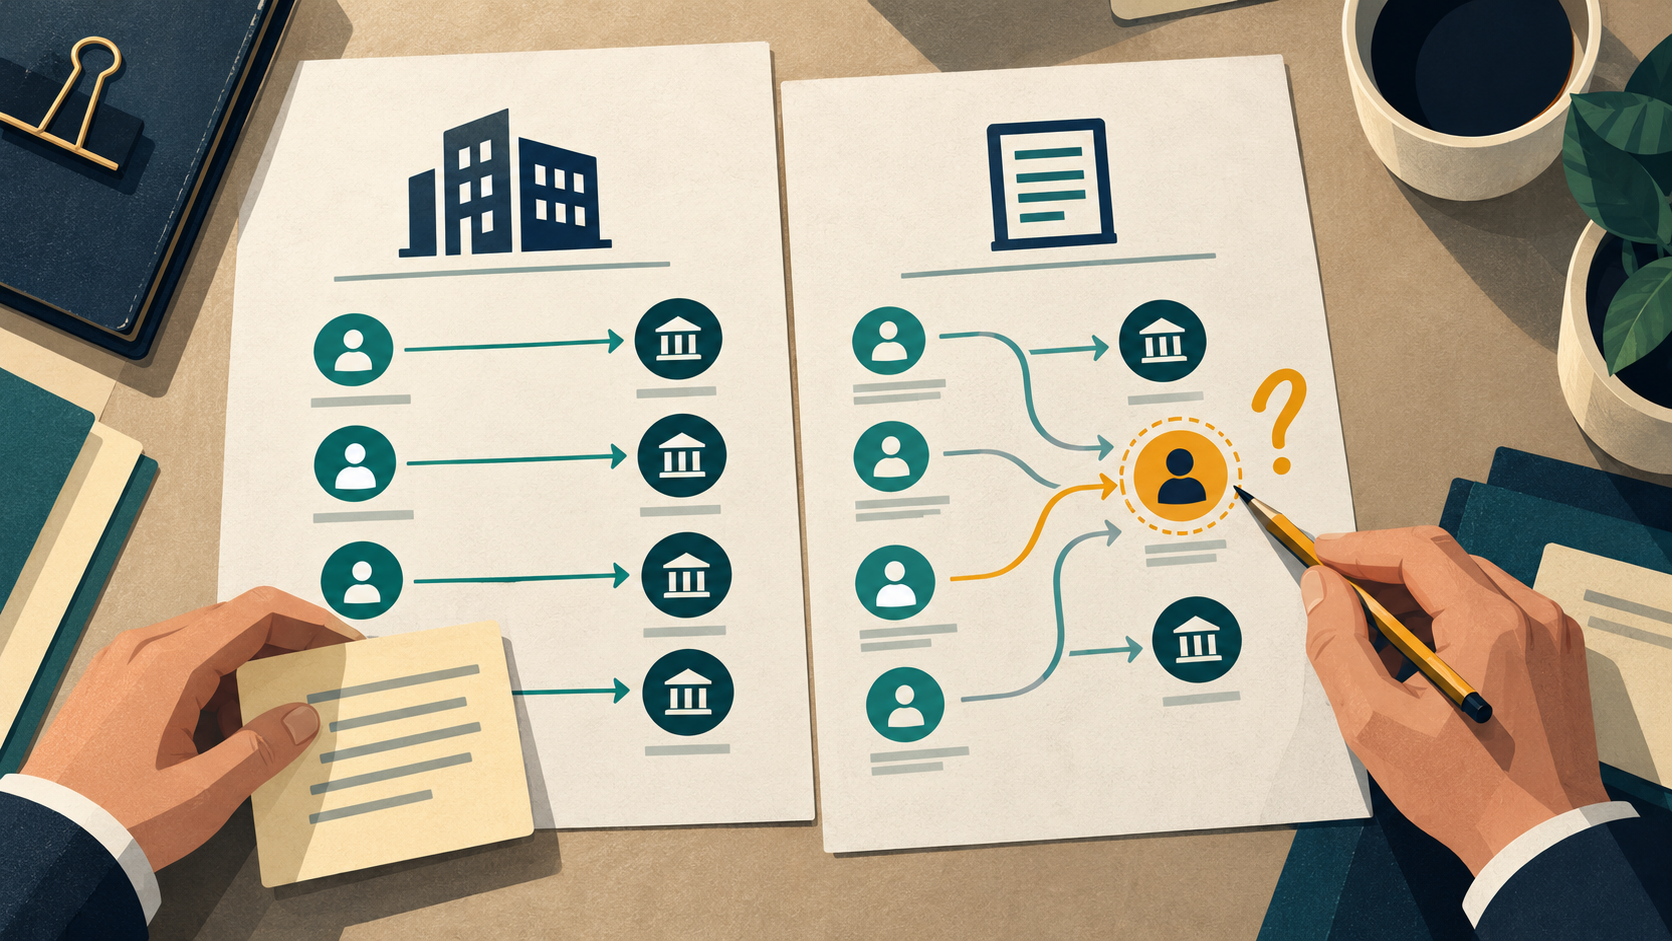
In the first case, a business receives funds from several unfamiliar senders and requests rapid onward transfers. Its known business model does not initially explain the new payment pattern. Participants should not vote on whether the customer is a criminal. They identify observable inconsistencies, explanations already available and unanswered questions. Ongoing monitoring under section 10 GwG links transactions to the customer profile, business activity and information held by the firm. An unusual payment is not automatically a fully assessed suspicion. Equally, a longstanding relationship is no justification for overlooking inconsistencies. What matters is an assessment that can be traced through the designated process.
Then provide a second piece of information: the relationship manager finds a plausible contract, but the contractual counterparty differs from the actual payment recipient. The handover must now be supplemented without rewriting the original observation. Useful notes separate the document received, the discrepancy identified and the clarification still outstanding. A sentence such as 'Contract received on Tuesday; recipient differs from the named counterparty; assessment pending' is more helpful than an unsupported accusation. The facilitator checks whether new information reaches the same case reference and whether anyone mistakenly treats an existing review status as definitive reassurance that no concern remains.
 AI-generated
Case two: Who is actually behind the instruction?
In the second case, someone acts for a corporate customer, presses for execution and provides inconsistent explanations about on whose behalf the transaction is being conducted. Ask participants to distinguish authority to act, beneficial ownership and transaction purpose. These concepts are related but not interchangeable. Employees record the specific inconsistency and follow the approved clarification route. They should neither declare missing documents irrelevant on their own authority nor assert suspicion merely because someone appears nervous. If the firm cannot meet required due diligence obligations, the consequences must be assessed under the applicable rules; an internal query does not automatically authorise continued processing.
Add a pressure scenario: a supposed senior manager calls and demands completion without further questions. Training on social engineering explains why authority and urgency can displace sound judgement. The practical response in this exercise is to verify identity through a known channel, avoid replacing the established process with an unfamiliar telephone number and involve the responsible function. Employees do not need to argue about motives. They need clear authority to escalate unresolved inconsistencies and a manager who supports that route. The learning comes from observing what they actually do under pressure, rather than from a general instruction to pay more attention.
Assess reporting, execution and customer communication separately
Internal escalation and external reporting are different steps. Section 43 GwG requires the obliged entity to report to the FIU without undue delay when the facts specified there are present, regardless of value or transaction amount. This creates neither a general waiting period for employees nor a requirement to prove an offence completely before reporting. The exercise should demonstrate how relevant information reaches the responsible function without avoidable delay. An internal completeness checklist must not cause a reportable matter to sit unattended. Missing information is identified as missing and supplemented through the designated process rather than used as a reason for indefinite postponement.
Execution of the transaction requires a separate assessment. Section 46 GwG sets rules for transactions that have been reported, alongside particular circumstances where postponement is impossible or could obstruct the prosecution of an alleged offence. Do not teach these provisions as 'always release after three days'. The responsible function must consider the actual conditions, decisions by the authorities and the current status. In the role-play, the back office must not infer permission to execute from an acknowledgement of receipt. It needs the documented decision required by the firm's responsibility framework. Uncertainty is resolved through the escalation route, not through an improvised exception.
Customer communication needs its own exercise step. The prohibition on disclosure in section 47 GwG covers, among other things, intended or submitted suspicious activity reports; statutory exceptions are not blanket permission for informal conversations. Employees use their firm's approved communication and do not disclose reporting details or internal assessments. Compare two possible answers: a factual statement about the status that may be communicated and an explanation that inadvertently reveals a report. The responsible function determines what may be said in the particular circumstances. A friendly tone does not make a substantively prohibited disclosure acceptable, and employees should know where to obtain guidance.
 AI-generated
Use a handover template with data minimisation
A useful internal template contains a case reference, observation time, relevant business relationship, factual trigger, available documents, open questions, transaction status and responsible recipient. Add any action already initiated and whose decision is required next. This is a recommended organisational aid, not a statutory form. Integrate it into the approved system rather than creating a parallel shadow archive. Practise the difference between 'the customer stated' and 'the document establishes'. A traceable initial escalation separates facts from assumptions so that the next person does not inadvertently treat an inference as verified information. The template should make that distinction easy to maintain.
Fictional names, synthetic account references and purpose-built documents are sufficient for training. Actual customer data should not be copied indiscriminately into presentations, general learning platforms or open AI tools. GDPR training for employees adds the questions of who may access which information and how purpose-limited processing is organised. Keep learning records separate from operational suspicion files: evidence of attendance does not need a complete customer history. If someone raises a real case during the session, the facilitator stops the open discussion and directs it to the protected channel. The classroom is not an alternative venue for handling live cases.
Evaluate the exercise without creating the wrong incentives
As a local design suggestion, use a short preparation phase, a role-based walkthrough and a joint debrief. Observe concrete criteria: was the inconsistency noticed, was the description factual, did the information reach the correct recipient and was an unauthorised release avoided? Also assess how participants handle missing information and customer questions. The number of reports generated is not a suitable personal performance target. It can encourage unnecessary reporting or concealment of difficult cases. Instead, document behavioural errors, gaps in responsibility and agreed improvements. A second walkthrough checks whether the correction changes actual behaviour rather than merely producing agreement in the meeting.
For traceable training records, capture the target group, learning objective, case version, attendance, observed decisions and any remedial instruction required. Passing a knowledge question does not automatically prove that someone can find the internal deputy route. Conversely, one error should not be interpreted as unreliability without context. Use the debrief to clarify operating instructions and assign specific improvements to accountable owners. When products, procedures or relevant risk patterns change, review whether the exercise needs updating. Ongoing instruction then becomes a maintained process rather than simply a recurring calendar entry containing exactly the same material year after year.
Another test concerns internal resistance. What happens if a manager tries to prevent an anomaly from being escalated? Employees need a suitable confidential route for reporting breaches of AML requirements. General guidance on whistleblower reporting channels can help explain the distinction, but such a channel is not automatically the operational AML escalation route or the FIU. The firm must explain each route's purpose and recipient. Ask participants to demonstrate both the normal case route and what happens when that route is obstructed. A channel name on a slide is insufficient if nobody knows how to access it or who provides cover.
Connect digital learning to your own procedure
A digital foundation course on AML prevention in the financial sector can establish shared terminology and typical decision situations. It does not replace the firm's risk assessment, reporting organisation or case-specific professional judgement. Before selecting a course, check that its roles, content and records match your institution. Supplement it with your actual contact routes, deputies and approved operating instructions. A useful next step is a pilot involving relationship management, the back office and the AML function around one fictional case. The pilot is complete when responsibilities are clear and identified gaps have accountable owners, not simply when participants make the final click in a course.
ConformBase
Turn knowledge into training that works.
Bring compliance, privacy and security awareness into a format your people want to complete, with certificates and audit-ready evidence.
Start free trialAsk about custom courses →